Sensitive Data Exposure is a common web security vulnerability where applications expose sensitive information such as passwords, credit card numbers, health records, or personal information due to poor security practices.
Examples:
Data sent over HTTP instead of HTTPS.
Passwords stored in plain text.
Weak or outdated encryption (e.g: using MD5 or SHA-1) instead use: bcrypt, scrypt, or Argon2 & salt.
Data leakage via verbose error messages, logs, or browser storage.
❌ Insecure: storing plaintext password
user_data = {
"username": "aiman",
"password": "mysecretpassword"
}
✅ Secure: hash + salt the password
import bcrypt, hashlib
password = "mysecretpassword"
salt = bcrypt.gensalt()
hashed = bcrypt.hashpw(password, salt)
username = "aiman"
hashed_username = hashlib.sha256(username.encode()).hexdigest()
I have known this vulnerability, taken the solution from internet
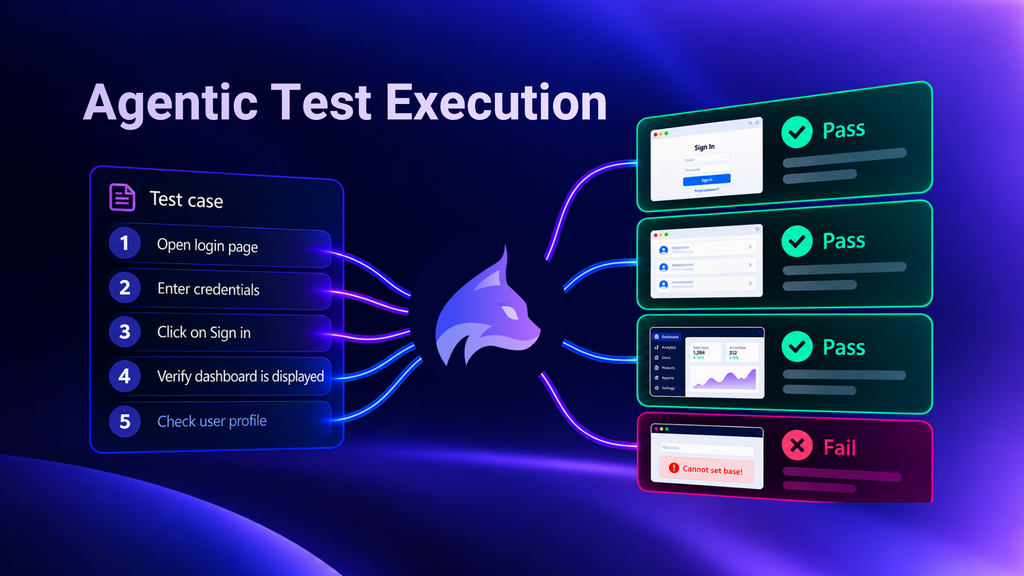
Lynqa executes your existing tests as written, no scripts or rewrites. Review step-by-step evidence. Start free.
BearQ continuously tests your app, reducing test maintenance and uncovering gaps scripted tests can miss.
Better than a generic video, see YOUR test, live, ready to show you what matters most: quality at scale.
With servers in >250 cities around the world, check your site for localization problems, broken GDPR banners, etc.
