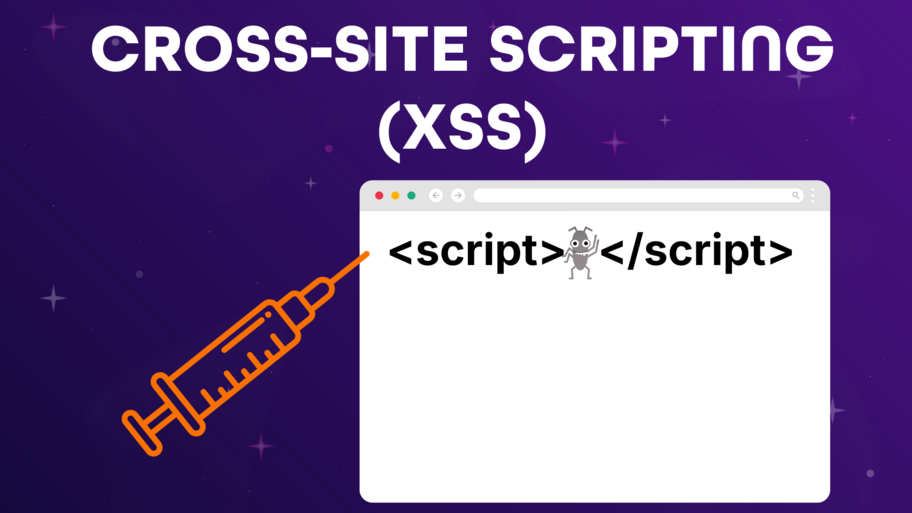
In this case, an attacker uses malicious scripting to interfere with a trusted website. Since the site doesn’t sanitize user input, the script can be executed in the user’s browser, generally to steal the cookies or session data.
Tester tip: Try using harmless scripts, such as in input fields or URLs. If it actually executes, then the site is vulnerable.
Pro tip: Always escape and validate all user inputs.
There are countless ways to show up and contribute. Which one will you try today?
Take this 7-question assessment to see where your QA team stands and get a plan for what to automate next.
With servers in >250 cities around the world, check your site for localization problems, broken GDPR banners, etc.
Centralized execution, reporting and insights in one place.
