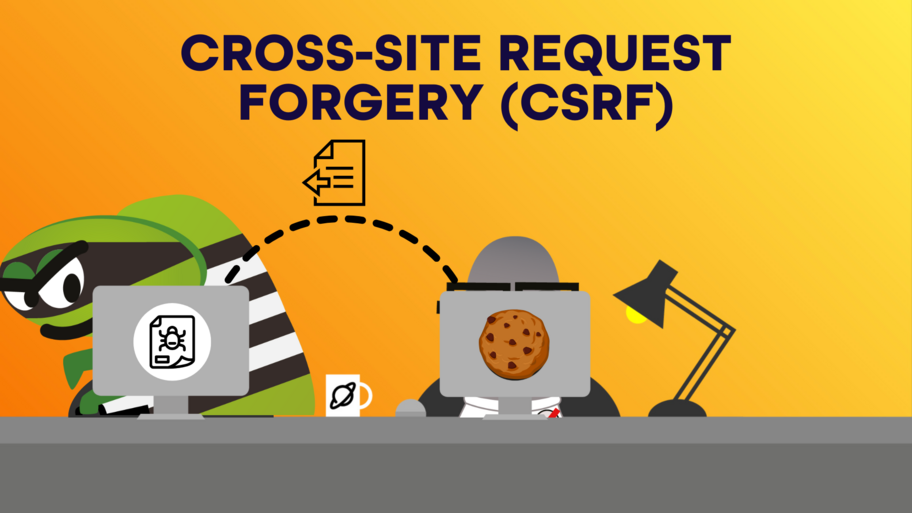
Cross-Site Request Forgery (CSRF) is when your browser gets tricked into doing something, like submitting a form using your login, without you knowing.It works because browsers send your cookies automatically, even if the request comes from another site. That means an attacker can abuse your login to perform actions on your behalf. Best way to stop it? Use CSRF tokens, set SameSite on cookies, and don’t trust requests just because the user’s logged in.
Better than a generic video, see YOUR test, live, ready to show you what matters most: quality at scale.
Genuine self-healing builds multi-attribute UI models. Here’s what to check before trusting the label.
With servers in >250 cities around the world, check your site for localization problems, broken GDPR banners, etc.
Getting tests that catch real failures is the hard part. Join us on Oct 8 and see how it's done.
