Zero-Day Vulnerability
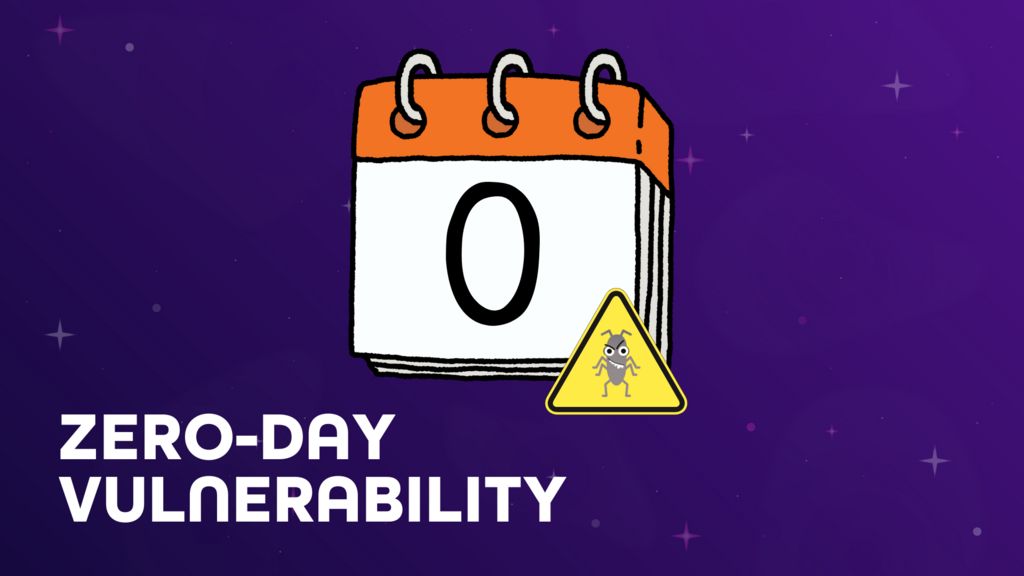
A “zero-day vulnerability” is an unknown or undiscovered security vulnerability that threat actors/attackers discover before the software provider does and is used to target the software, hardware or firmware with malicious code. The term "Zero-Day" is used when security teams are unaware of their software vulnerability and they’ve had “0” days to work on a security patch or an update to fix the issue. This means vulnerabilities can lay undetected for days, months or years until someone (usually a malicious actor) finds it. A zero-day vulnerability is a potential chink in your armor that exists up until it’s patched or removed, meaning for the entire time it takes to develop, test, and deploy a fix the company and those that use it’s products/services are vulnerable to attack.
18th September 2025
A security flaw in software, hardware, or firmware that is unknown to the vendor and therefore has no official patch or fix. The vulnerability may have existed for a long time before discovery.
Zero day refers to the vendor's awareness, not the flaw's age.
Zero day refers to the vendor's awareness, not the flaw's age.
A researcher discovers an undocumented memory corruption bug in a popular browser. Since the vendor doesn't know about it yet, it's a zero-day vulnerability.
4th May 2026
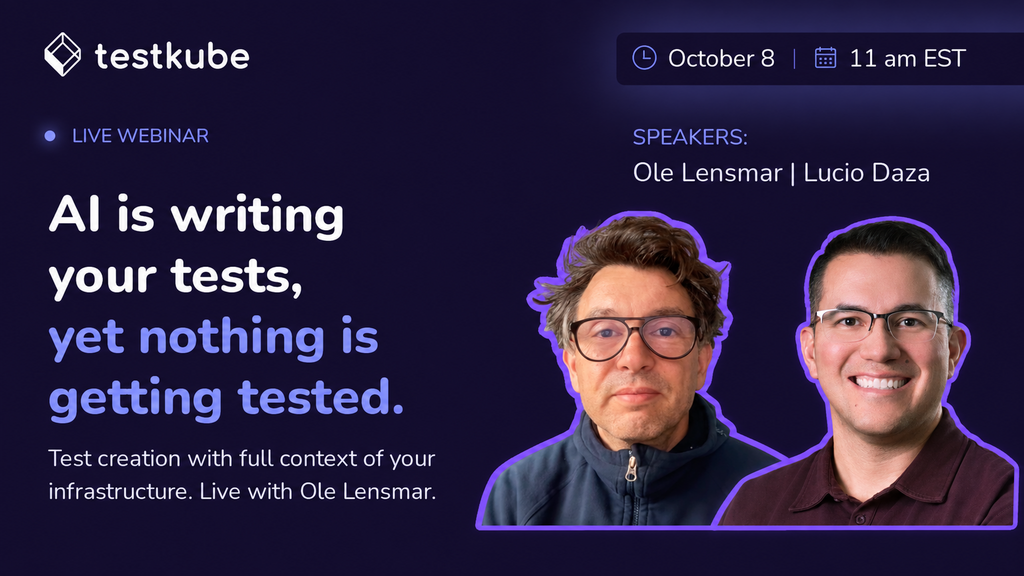
Getting tests that catch real failures is the hard part. Watch the recording now on demand!
Explore MoT

Tue, 19 Jan 2027
Test Forward is one afternoon at Station F with the QA and engineering people closing that gap in their own teams.
Boost your career in software testing with the MoT Software Testing Essentials Certificate. Learn essential skills, from basic testing techniques to advanced risk analysis, crafted by industry experts.
Debrief the week in Quality via a community radio show hosted by Simon Tomes and members of the community
