Application Security is a hot topic and increasingly software testers are being asked to carry out “security tests”; sometimes this is in addition to external security tests but often instead of. Despite the widespread availability of resources on security testing, much of it focuses on techniques so it can be difficult for testers to know where to start and what is important to their context.
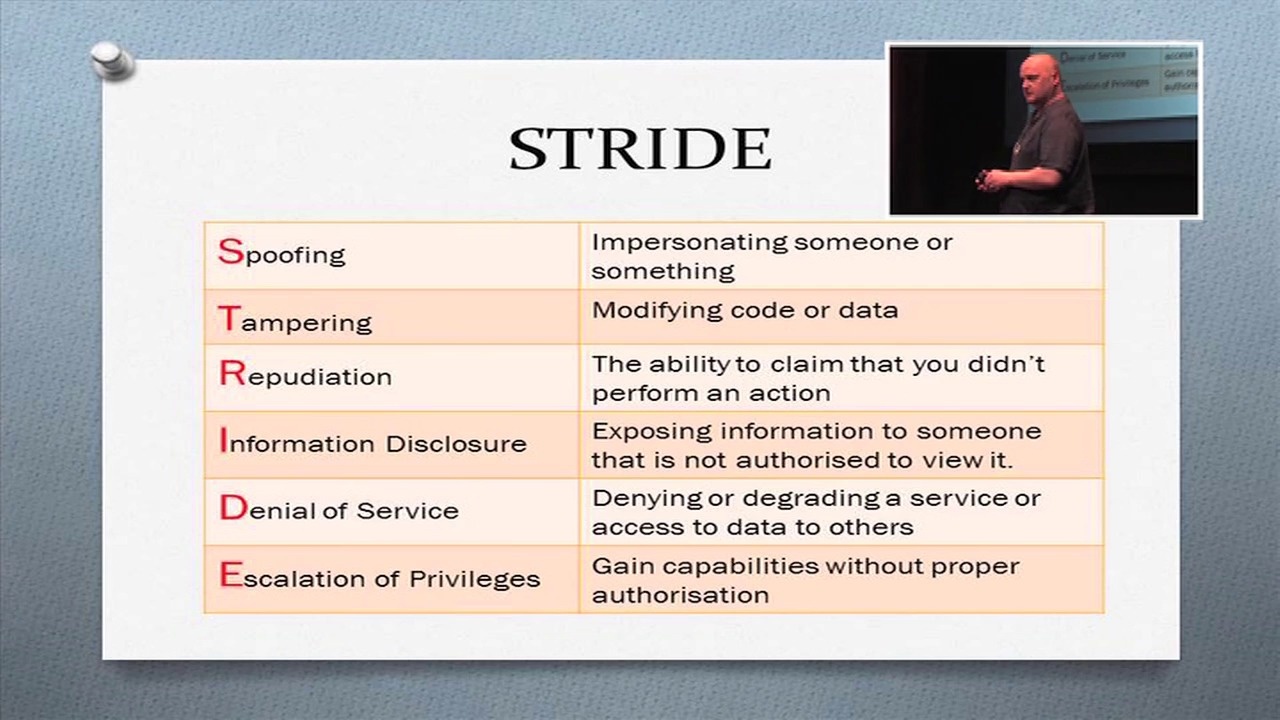
Building a Threat Model can help testers formulate a more context driven approach to security testing and help frame these tests by linking your application/assets to possible threats and vulnerabilities, to the tests you are carrying out (or not) and the techniques needed to implement them.
Your test cases are the context AI agents are missing. See how the Testmo MCP connects them in this free webinar.
Explore MoT
Learn how to structure and organize test management data as an AI-ready foundation that gives AI systems richer context for testing insights and workflows.
Mitigate security risks by building simple security testing techniques into your daily routine
Into the MoTaverse is a podcast by Ministry of Testing, hosted by Rosie Sherry, exploring the people, insights, and systems shaping quality in modern software teams.

Comments