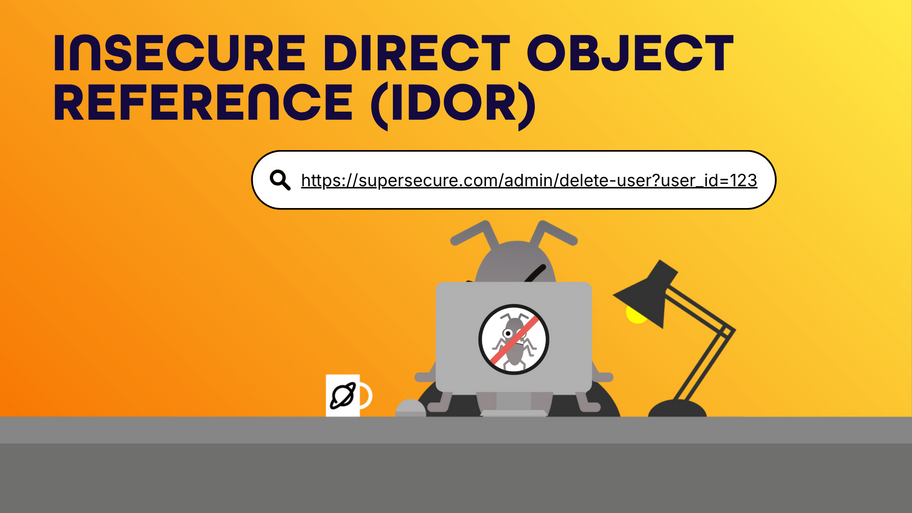
IDOR is when an application exposes internal objects (like user IDs, files, or records) in a way that lets users access data they shouldn’t, for example, by simply changing a value in the URL. IDOR is one of the most common vulnerabilities found in bug bounty programs, probably “THE ONE” to know. Example: If a URL is https://example.com/profile?user_id=123And the application doesn’t verify if the user accessing the page is actually user 123; someone could change the user_id to 456 and access that user’s profile and edit it.

Generative AI apps and integrations are growing fast and so are the injection attacks. This time it's through harmless-looking plain text, aka prompts.

The words we use every day matter, let's tweak them!

Generalist in software testing is a tester whose skills, interests, or habits are varied or unspecialized
A person who knows a bit about everything in testing.

Getting ready to Puzzle for Success!
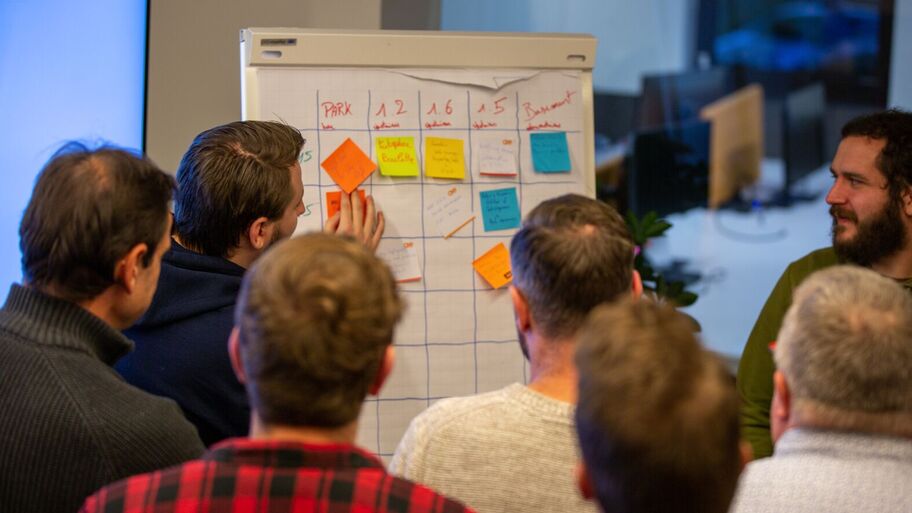
MoT Belgium doing Open Space

Kristof chats to Julie about the future plans for Ranorex in 2024


Kristoff chats with Dennis Nelson about the mabl university and how it all works.

Kristof is joined by Jake Cave to learn what Enov8 are up to at the moment

Kristof is joined by Rohit Gupta to learn what Enov8 are up to at the moment

Kristof is joined by Aaron Stearns to learn what Ranorex are up to at the moment

Taking a quick look at Test Automation Trends for 2023
Wrong arguments, duplicate calls, skipped checks. Learn how to validate every action your MCP agent takes.
BearQ continuously tests your app, reducing test maintenance and uncovering gaps scripted tests can miss.
Better than a generic video, see YOUR test, live, ready to show you what matters most: quality at scale.
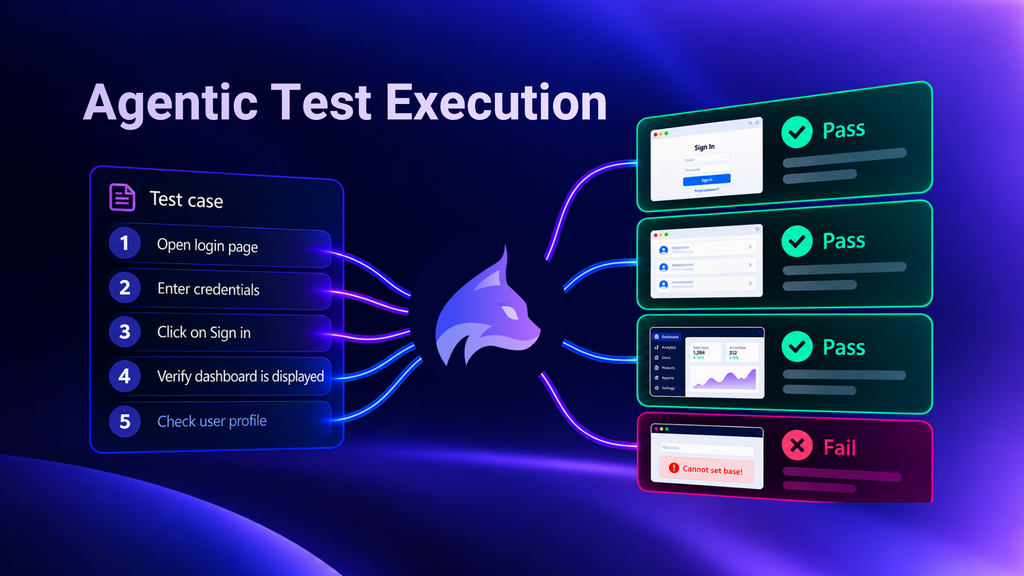
Lynqa executes your existing tests as written, no scripts or rewrites. Review step-by-step evidence. Start free.
