Jesper Ottosen
Jesper Ottosen
Principal Consultant
him/his
Jesper has been around the MoT community from the start, frequently passing by the Club and Slack. For more than 10 years he has provided 300+ blogposts on all things testing. 🌻
🎂 MoTaBirthday | December 4, 2014
Open To
Teach
Speak
Mentor
Podcasting
Meet at MoTaCon 2026
Write
So with MotaCon you are all inspired and informed
The relevant industry Information about how to solve challenges
The Opportunity to solve the challenge
The growth Mindset to embrace challeng...
1 Oct
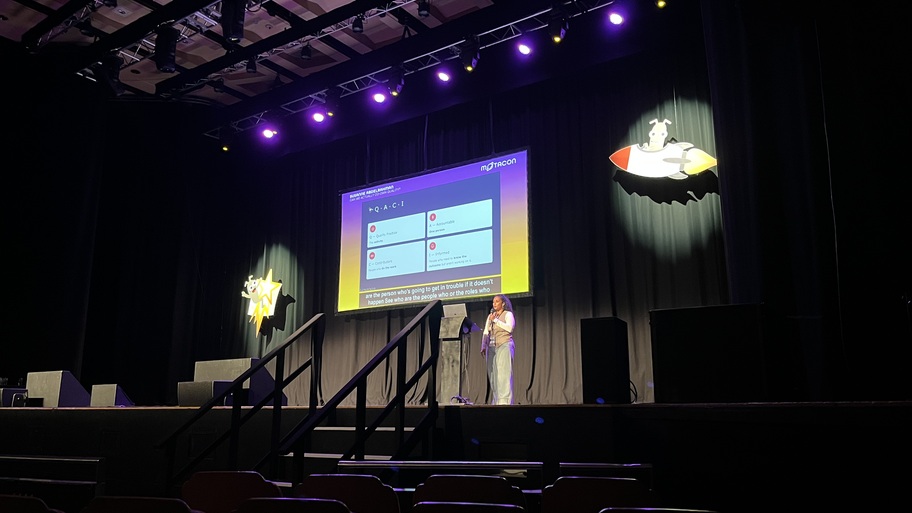
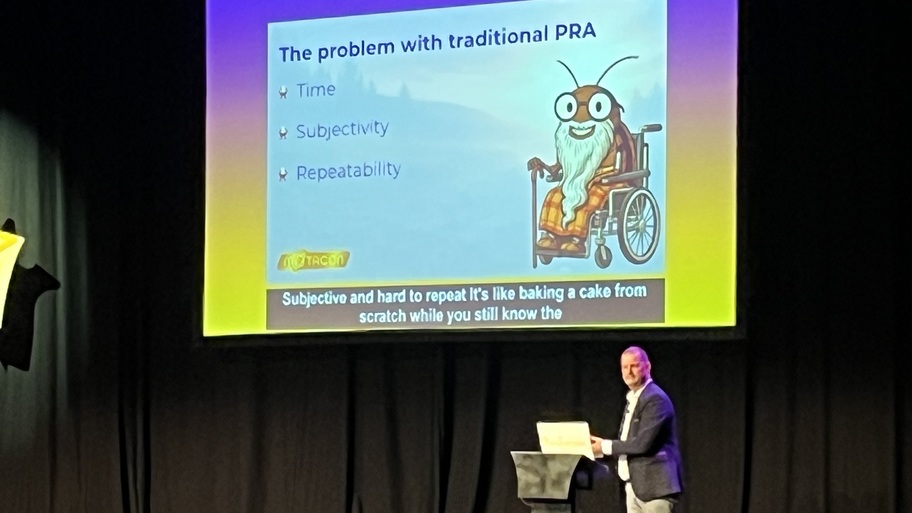
So much this! I’m bringing home that we can get good enough PRA from AI analysis of the system under test
1 Oct
How is friction helping and not helping software engineering and testing teams?
20 Feb

AI can transform our love for curiousity, documentation and knowledge management
26 Nov
Explore ways to use imagination to move past bottlenecks and grow new quality leaders
4 Dec
Shift your mindset from documenting testing to influencing quality with meaningful conversations.
7 Nov
Ilities
The 'ilities is the informal name for all the system quality attributes, that usually end in 'ility.Accessability, scalability, functionality, reliability....For a full list see the reference
Nemawashi
Slowly and indirectly building support and alignment.A way to approach to delivering value more reliably and sustainably look like https://www.ministryoftesting.com/moments/what-does-delivering-value-more-reliably-and-sustainably-look-like From Wikipedia:Nemawashi (根回し) is an informal Japanese business process of laying the foundation for some proposed change or project by talking to the people concerned and gathering support and feedback before a formal announcement.
Injection Flaws
Injections are about maliciously putting things where they’re not supposed to go. Originally, for input fields, like text boxes or forms, where someone could inject malicious code. One of the most famous examples is from the classic XKCD comic “Exploits of a Mom”, where a child is registered at school with a name that includes a bit of code, and it accidentally causes the school’s database to break. But it's not just about forms anymore. Prompt injections are similar in nature. Anywhere a user can put stuff is prone to injection flaws.Tip: Always validate and sanitize anything users can send.
Supply Chain Attack
Your web app will depend on libraries and third-party components outside your control. For example, Social media (SoMe) trackers and CSS or similar plugins. Over time, they might be insecure or outdated. This is known as a supply chain attack, when something you already trust becomes the way attackers get in. Tip: Keep a list of them and the last working version on your end. Examples: One famous example was log4j and another was SolarWinds.
Comments
(20)
solving the problem of clicking a problem
The rope is not the problem when climbing a mountain
Dyslexia Blog
🌻
New Job, New Chapter: Stepping Into Healthcare QA! 🩺
My experience is mostly pharma/medicine production, but still heavily regulated. One thing I learned was that in that context "QA" is a whole other profession than we we testing people usually would usually think.
I've Configured Things You Wouldn't Believe
awwh. <3
I've Configured Things You Wouldn't Believe
that reminds me: I’ve seen things you people wouldn’t believe. Browser wars off the shoulders of the millennium, mainframes glitter black-green and management shooting for delivery gates. All those moments are not lost in time, but curated and internalized.
...
https://www.ministryoftesting.com/satellites/keeping-track
Culture’s Consequences: Comparing Values, Behaviors, Institutions, and Organizations Across Nations
(digitalcommons.usu.edu)
30 Sep
Not registered for any upcoming events
Meeting Susanne Abdelrahmen at MoTacon 2026
I just want to give a shoutout to Susanne. My first "gig" with the MoTaverse was a LwQ podcast in 2025 with Rosie that started from a comment I added to Rosies LinkedIn post asking for help around ...
Contributor thanking
32 minutes ago
Thanks for your contribution
Meeting Susanne Abdelrahmen at MoTacon 2026
Community Star
32 minutes ago
Thanks for your contribution
Meeting Susanne Abdelrahmen at MoTacon 2026
Community Star
32 minutes ago
